Ars Technica
New bootloader lets you take the "Meta" out of the original Meta Quest
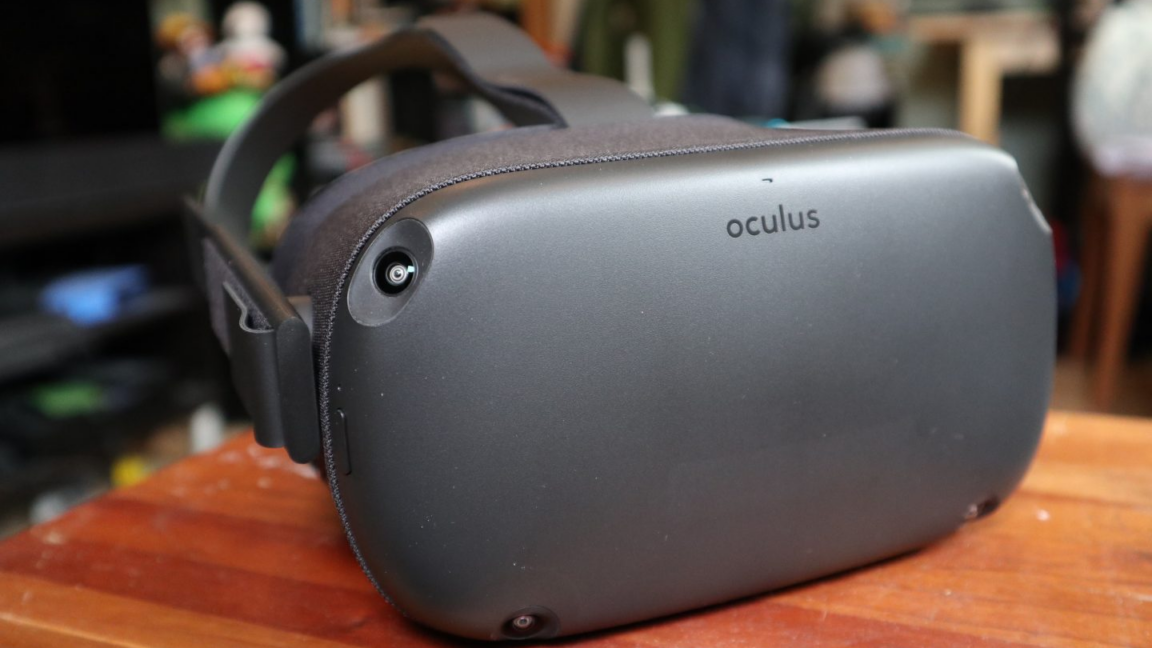
The QuestStack project combines known fastboot vulnerabilities on the original Quest into a privilege-escalation chain that grants full root access via a new bootloader, which can be triggered through a web interface after connecting the headset to a PC. This exploit removes dependence on Meta’s servers, allowing sideloading of apps and initial setup without a Meta Developer account or Developer Mode.